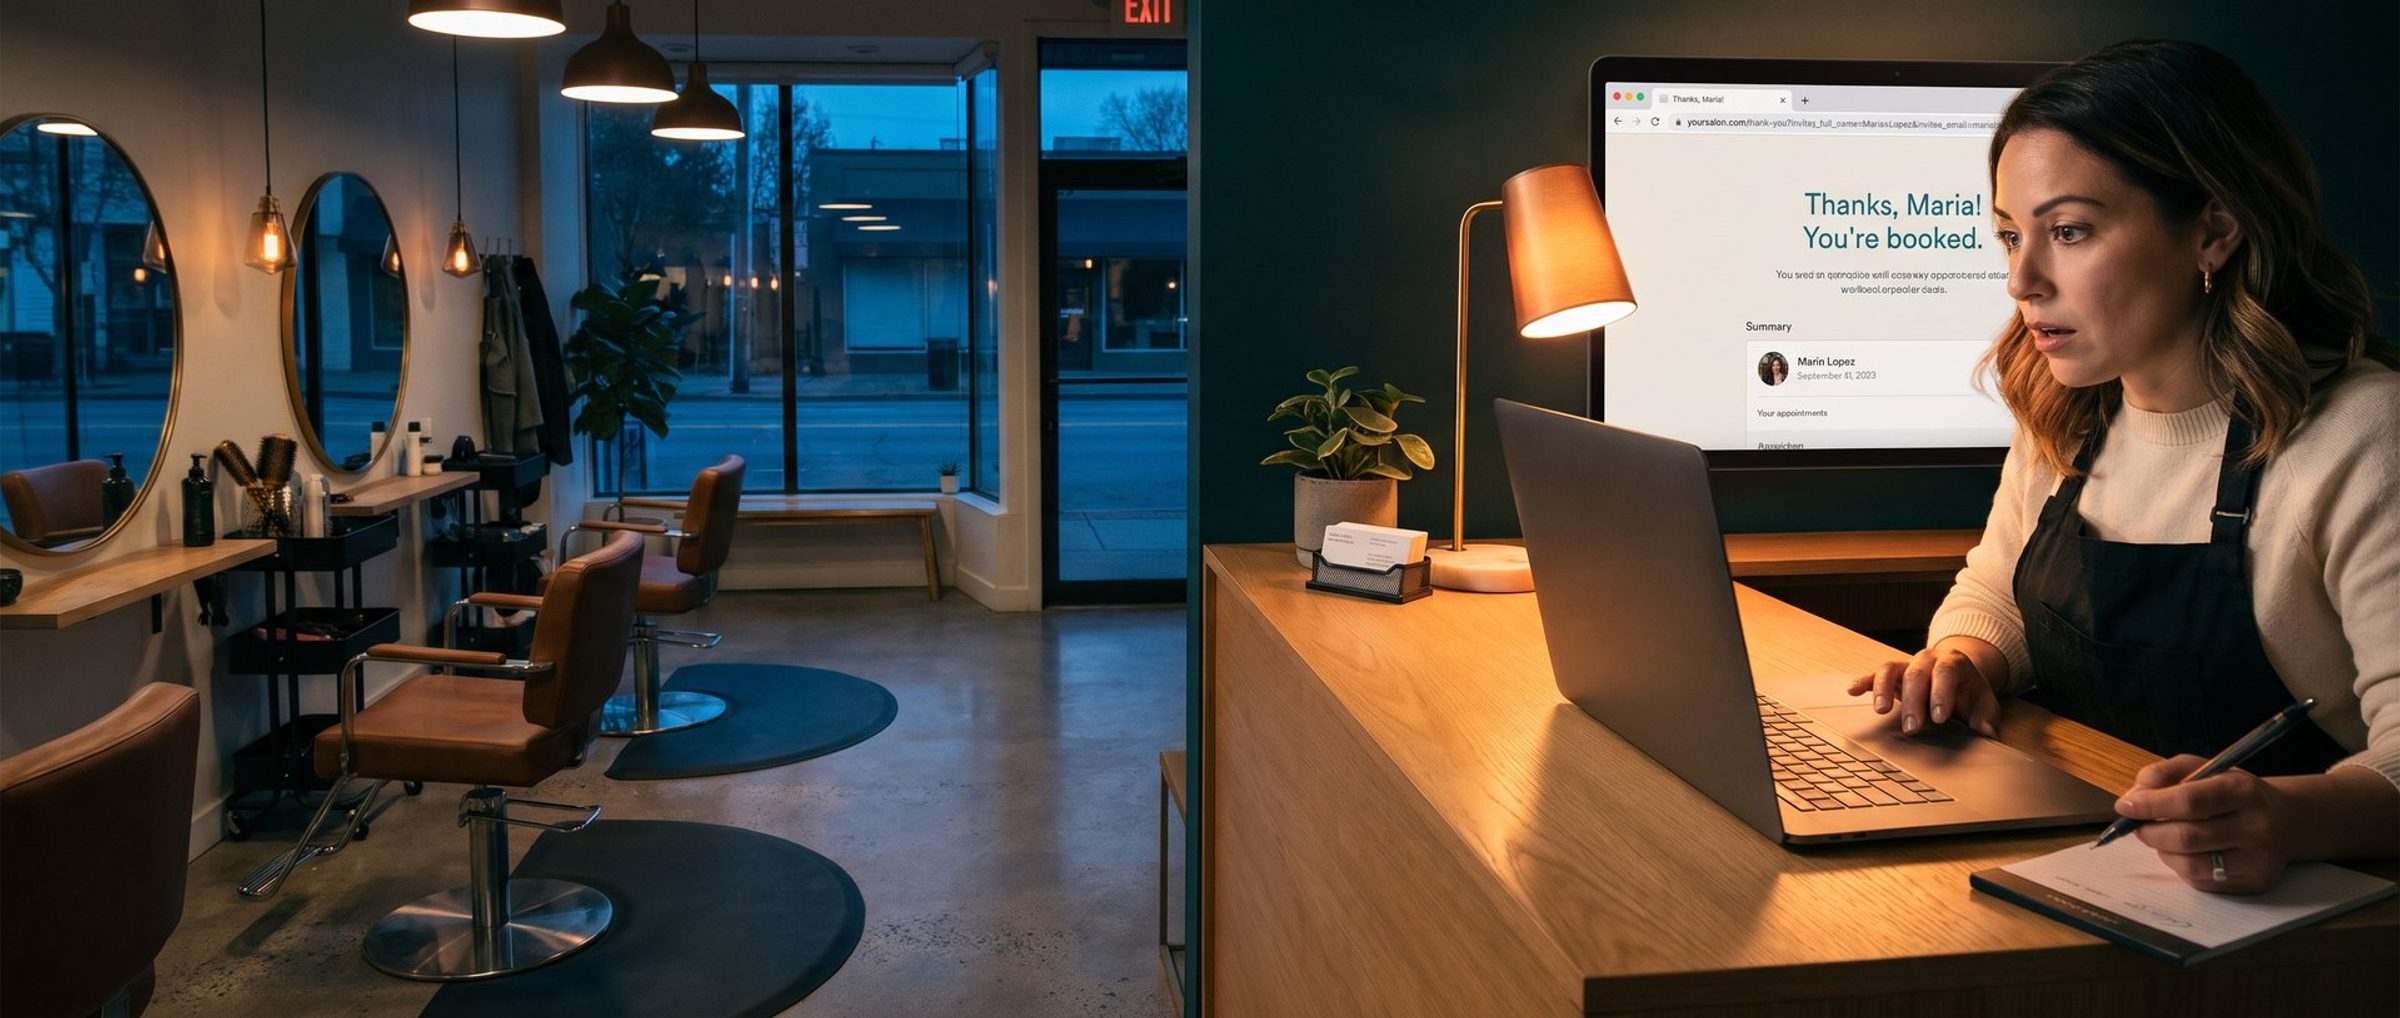
Someone books a consultation on your website. The calendar does its job, the thank-you page loads, and if you glance at the address bar you will see something like this:
yoursite.com/thank-you?invitee_full_name=Maria+Lopez&invitee_email=maria%40gmail.com
Nothing looks broken. The booking went through, Maria got her confirmation, and the conversion counted in Google Ads. That last part is the problem. The tag that counted the conversion sits on that page, it reads the page's address, and the address now contains Maria's name and email. You just handed both to Google.
Google's data collection and use policy for advertisers says you may not do that. Personal details are not allowed to reach Google through its remarketing tags, its conversion tags or your product feeds. And the most common way a small business breaks the rule is not a shady data deal. It is a thank-you page that copies form answers into its own web address, set up years ago by whoever built the site, and never looked at since.
The good news is that this is one of the easiest policy problems you will ever fix, and you can check for it yourself in about ten minutes.
Google's Tag Reads the Whole Address, Including Everything After the Question Mark
Every web address has two parts. The part before the question mark says which page you are on. The part after it, the query string, carries extra information in pairs: "name=value", joined by ampersands. Plenty of that information is harmless, like the tracking codes on your ads or a product color. The trouble starts when a website uses the query string to carry what a customer just typed into a form.
Google's tags report the address of the page they fire on. That is how Google knows a conversion happened on your thank-you page and not your homepage, and how a remarketing list knows who visited your pricing page. A tag doesn't pick out the safe parts of the address. Whatever is in the query string goes along for the ride.
Google's own troubleshooting notes for this policy name the usual culprits: web forms, login pages and email marketing links. On a small business website, that usually means one of four things.
- A form that submits with GET instead of POST. It's a single setting in the form's code. GET puts every field into the address bar. POST sends the same fields quietly in the background. Older custom forms and some cheap plugins still use GET.
- A booking tool that passes details to your thank-you page. Calendly has a checkbox called "Pass event details to your redirected page." Tick it and Calendly adds the booking to the end of your redirect address, including the invitee's email, full name and, if they gave one, their text-reminder phone number. Calendly's own help page suggests using it to track conversions, which is exactly where the conversion tag is waiting.
- A form plugin that forwards answers to the next page. Gravity Forms, one of the most common WordPress form plugins, has a confirmation option called "Pass Field Data via Query String." It is a useful feature for personalizing a page. It also writes whatever fields you choose straight into the address.
- An email newsletter that puts the subscriber's address in its links. Some email setups add the reader's email to every link so the site can recognize them. When they click through, the email lands in the address of a page that has your Google tag on it.
It helps to know what Google actually counts as personal information here, because it is narrower than most privacy laws. Google's definition is information that could identify, contact or precisely locate a person on its own: email addresses, mailing addresses, phone numbers, precise locations, and full names or usernames. IP addresses and cookie IDs are not on the list. Their example could have been written for this article: if a page sends its address to Google, that address must not include an email.
Google's Data Policy Bans Five Practices. Two of Them Catch Small Businesses.
The data collection and use policy is short. It names five things you can't do, and for a typical US small business they are not equally risky.
1. Collecting sensitive numbers on an insecure page. Google bans collecting things like card numbers, bank details, Social Security numbers, tax IDs, driver's license numbers or health care numbers on a page without SSL, the security certificate that turns "http://" into "https://". Most site builders and hosts turn SSL on by default now, so this mostly catches old sites and forgotten subdomains. It takes five seconds to rule out: load your form page and look for "https" and the padlock.
2. Sending personal information to Google through its tags or feeds. This is the one this article is about, and the one most likely to apply to you, because it happens by accident. Google's example is word for word the thank-you page problem: sharing users' email addresses through URLs that have remarketing tags on them.
3. Misusing personal information. You can't use customer data in ways customers didn't agree to. Google's examples are reselling contact information and using a customer's photo in an ad without their consent. The same section bans ads that act like they know you. Google's examples are "Hello John Smith - buy flowers here!" and "You're buried in debt. Get help today." For a small business, the realistic version of this is the customer testimonial photo nobody signed off on. If a happy client's face is in your ad, get their permission in writing.
4. Ignoring consent rules for European and UK visitors. If you advertise to people in the European Economic Area or the UK, you need their consent before using cookies for remarketing or conversion tracking, and your consent banner has to link to Google's information about how it handles data. A plumber who only advertises in Ohio can skip this one. An online store that ships to London cannot.
5. Setting cookies on Google's own domains. Nobody but Google may set cookies on domains like doubleclick.net. If you run a small business and aren't building ad technology, you will never touch this.
So for most owners, the real exposure is items 2 and 3. One is a technical leak you can't see unless you look for it. The other is a judgment call you make every time you put a real customer into an ad.
Google Warns Before It Suspends. It Takes Your Remarketing Lists First.
Policy articles love the word "suspension," so let's be precise about what actually happens here.
Google sorts violations into two kinds. Egregious ones, things so serious they are illegal or cause real harm, get an account suspended immediately with no warning. This policy is not one of those. Its own page says a violation will not lead to immediate suspension, and that a warning will be issued at least 7 days before any suspension. For the personal-information rule in particular, Google sends a breach notice that lists the addresses on your site where it found the problem. That list is genuinely useful, because it tells you which form or page to fix.
Suspension is not the first thing to go, though. The policy says remarketing lists that don't comply will be disabled. That covers the audiences built from your site visitors and any combinations built from them. For an owner who has spent a year building a list of everyone who looked at the pricing page, that is a real loss, and it can happen without a single ad being disapproved.
If the problem keeps happening, Google's general enforcement rules take over: strikes for repeat violations of the same policy, up to three, with penalties increasing at each one, and then suspension. A suspension is also contagious. Google says related accounts, such as ones that share a payment method, get suspended with it, and any new account you open is suspended automatically. We covered the rest of that landscape, including the billing and login mistakes that take down far more small accounts than ad content does, in Your Ad Account Is Not Yours.
It is also worth hearing from someone who fixes suspensions for a living. John Horn of StubGroup, a firm that specializes in untangling Google Ads suspensions and policy problems, says on his channel that he rarely sees flags for this policy and couldn't recall ever seeing the personal-information one. Take that seriously. This is not a time bomb under every small business account.
But notice what that means. A problem that is rarely enforced and invisible from the dashboard is exactly the kind that sits on a website for five years. Meanwhile every other tool on that page, from Meta's pixel to the chat widget to whatever analytics script a past developer added, is receiving the same names and emails. Google's rule is just the one with a policy page attached.
Your Own Test Booking Shows the Leak in Ten Minutes
You don't need a developer to find out whether you have this problem. You need your own website, a test email address and a few minutes.
Fill out your own forms. Go through every form and booking link on your site the way a customer would. Use a test address you'd recognize, something like "test@" your own domain, and a fake name. When the thank-you page loads, click into the address bar and read the whole thing. If you see your test name, email or phone number anywhere in it, you've found a leak. Do this for every form, not just the main contact form: quote requests, booking widgets, newsletter signups, downloads.
Search GA4 for the @ sign. Every email address contains an @, which makes them easy to find. In Google Analytics 4, go to Explore and start a blank exploration. Add the dimension Page path + query string (or Page location) and a metric like Event count, drag both into the table, then filter the dimension to rows that contain "@". Run the filter again for the names of your query parameters, like "email=" or "name=". Set the date range as far back as your data goes. If anything comes back, the dimension shows you exactly which page is doing it.
Check the settings that cause it. In Calendly, open each event type, go to the confirmation page section and see whether "Pass event details to your redirected page" is on. In your form plugin, look at each form's confirmation or redirect settings for anything that passes field data to the next page. Then send yourself a test newsletter and hover over the links before you click. If your email address is visible in the link, so is everyone else's.
If all three checks come back clean, you're done, and you can stop worrying about this policy.
The Leak Lives in the Form. A Report Filter Won't Stop It.
If you found a leak, the fix belongs at the source, and it's usually small.
Stop the website from writing personal details into the address. For a hand-built form, that means changing it to submit with POST instead of GET, which is a one-word change in the form's code and the exact fix Google's own instructions give. For Calendly, untick "Pass event details to your redirected page" unless something on your thank-you page truly depends on it. For Gravity Forms and similar plugins, remove the personal fields from the confirmation's query string.
If the next page genuinely needs to know who someone is, send an ID instead. Google's suggested fix is a unique number standing in for the person. A page that used to say "my_settings/sample@email.com" says "my_settings/43231" instead, and your own system looks up who 43231 is. Your developer will know how to do this in an afternoon. Calendly also passes an "invitee_uuid", a random ID, which is enough for most follow-up tools.
If Google sent you a notice, tell it you fixed it. The policy page links to a response form for exactly this. After you submit it, Google checks your site again and sends another notice within two weeks either confirming the fix or listing the addresses that are still sending personal data.
Treat GA4's data redaction as a seatbelt, not the fix. GA4 has a setting, under Admin, Data streams, then Redact data, that strips email addresses and any query parameters you name before data reaches Analytics. Turn it on. New properties have email redaction on by default, but older ones need it switched on by hand. Then understand its limits. Google describes it as best effort, it only works on web data streams, and it can misfire on text that merely looks like an email. As Julius Fedorovicius of Analytics Mania points out, it also doesn't clean up data you've already collected, and it only protects what goes to Analytics. It is a GA4 setting, so don't count on it for your Google Ads tag, and Meta's pixel, your chat tool and everything else on the page still read the same address. That is why the fix has to happen in the form.
Health businesses should take this section twice as seriously. On a health site, a page address can reveal a condition as well as an identity, and Meta enforces its own version of the same rule. We walked through that in Your Health Business Cannot Retarget People the Normal Way, and the same rule of thumb applies: the leak is usually the URL, not the tag.
Enhanced Conversions Sends Google the Email the Way the Policy Allows
Here is the irony behind most of these leaks: somebody wanted better tracking. They wanted to know which ad produced which lead, and passing the email along seemed like a clever way to do it.
Google agrees that tying a conversion to a real customer makes your data better. It just wants it done through the front door. The same policy that bans sending personal details through tags makes a specific exception for enhanced conversions, Customer Match and store sales, which run under Google's data processing terms. With enhanced conversions, the email a customer types into your form is scrambled with a one-way hash called SHA256 before it is sent, and Google matches it to the Google account the person was signed in to when they engaged with your ad. You get better attribution, and nobody's address ends up in a page URL for every script on the site to read.
Customer Match works the same way in the other direction. You upload your own customer list to target or exclude those people, and Google handles it under the same terms. We've made the case for why that list is the best audience you can give Google Ads, and it is a far better use of your customers' emails than a query string.
Two cautions keep this honest. Both features come with their own customer data policies, including a privacy policy that tells your customers you share their data this way. And sending Google better data doesn't make its conversion numbers match your other tools. Consent mode and modeled conversions are a separate story, which we covered in GA4 Says 40 Conversions. Google Ads Says 61. Both Are Right.
Checking Your Thank-You Page Takes Ten Minutes. Most Accounts Never Do It.
Most of the advice you'll read about Google Ads is about getting more out of the platform. This is one of the rare jobs that is about not giving it something you were never supposed to send. It takes ten minutes to check, usually an afternoon to fix, and it protects the remarketing lists you've spent months building, along with your customers' trust in what you do with their information.
If you'd rather someone look over the forms, tags and conversion setup behind your ads for you, that check is part of how we start every Google Ads management account. If you'd rather do it yourself, everything you need is on this page.